SHOPPING FRANCE
Personal Shopper & Cross-Border COD E-Commerce (58 Wilayas) + Active Honeypot Data-Poisoning Defense (/demo)
shoppingfrance.store
Lead Full-Stack Developer & Security Architect
2026
CodeIgniter 4.5 · PHP 8.2 · MySQL · Tailwind CSS
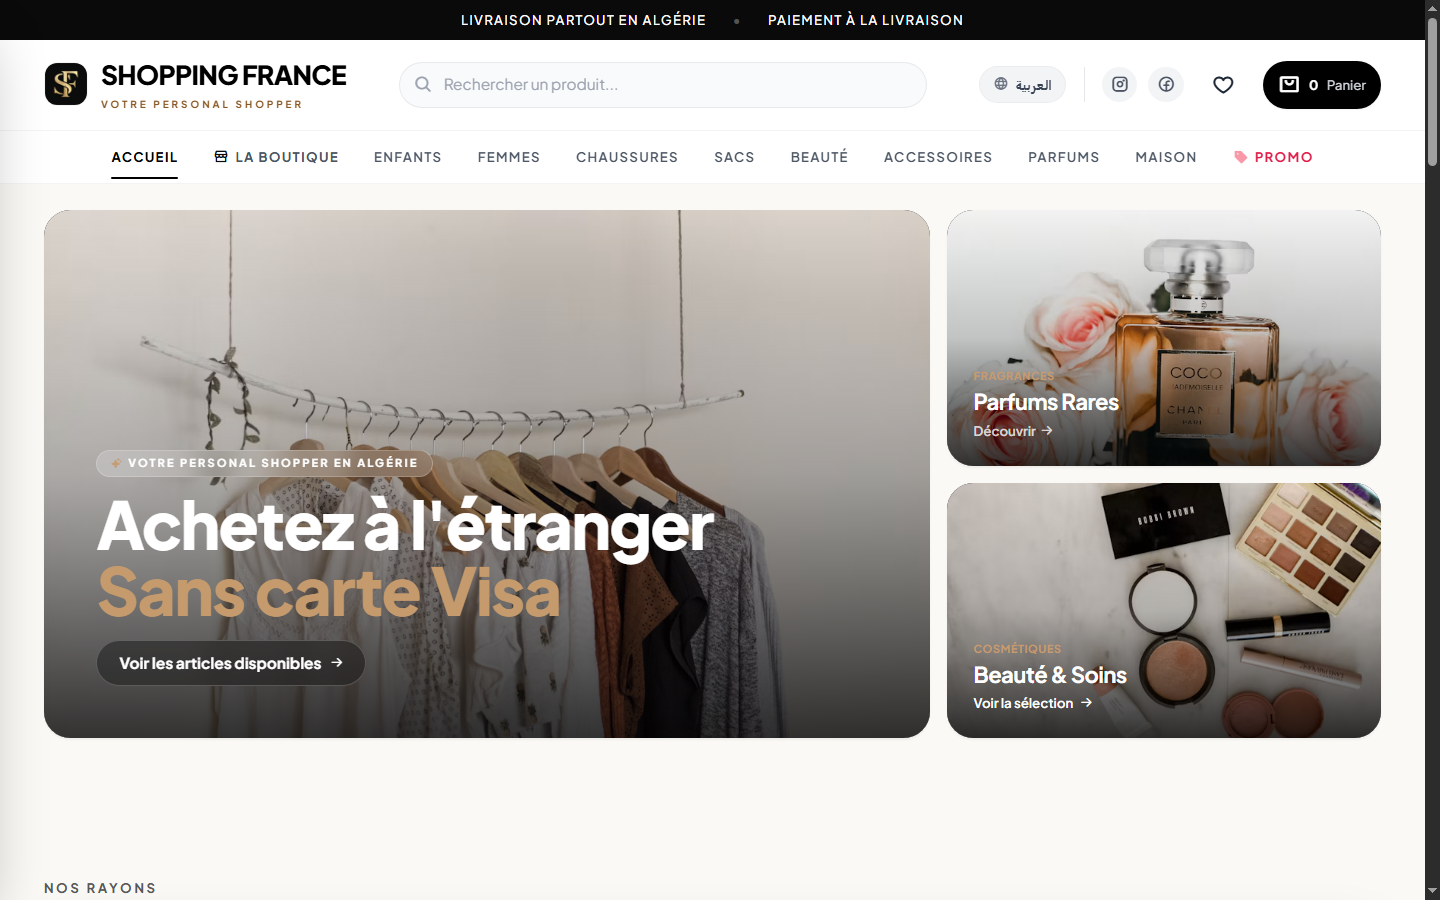
Live Storefront + /demo Console
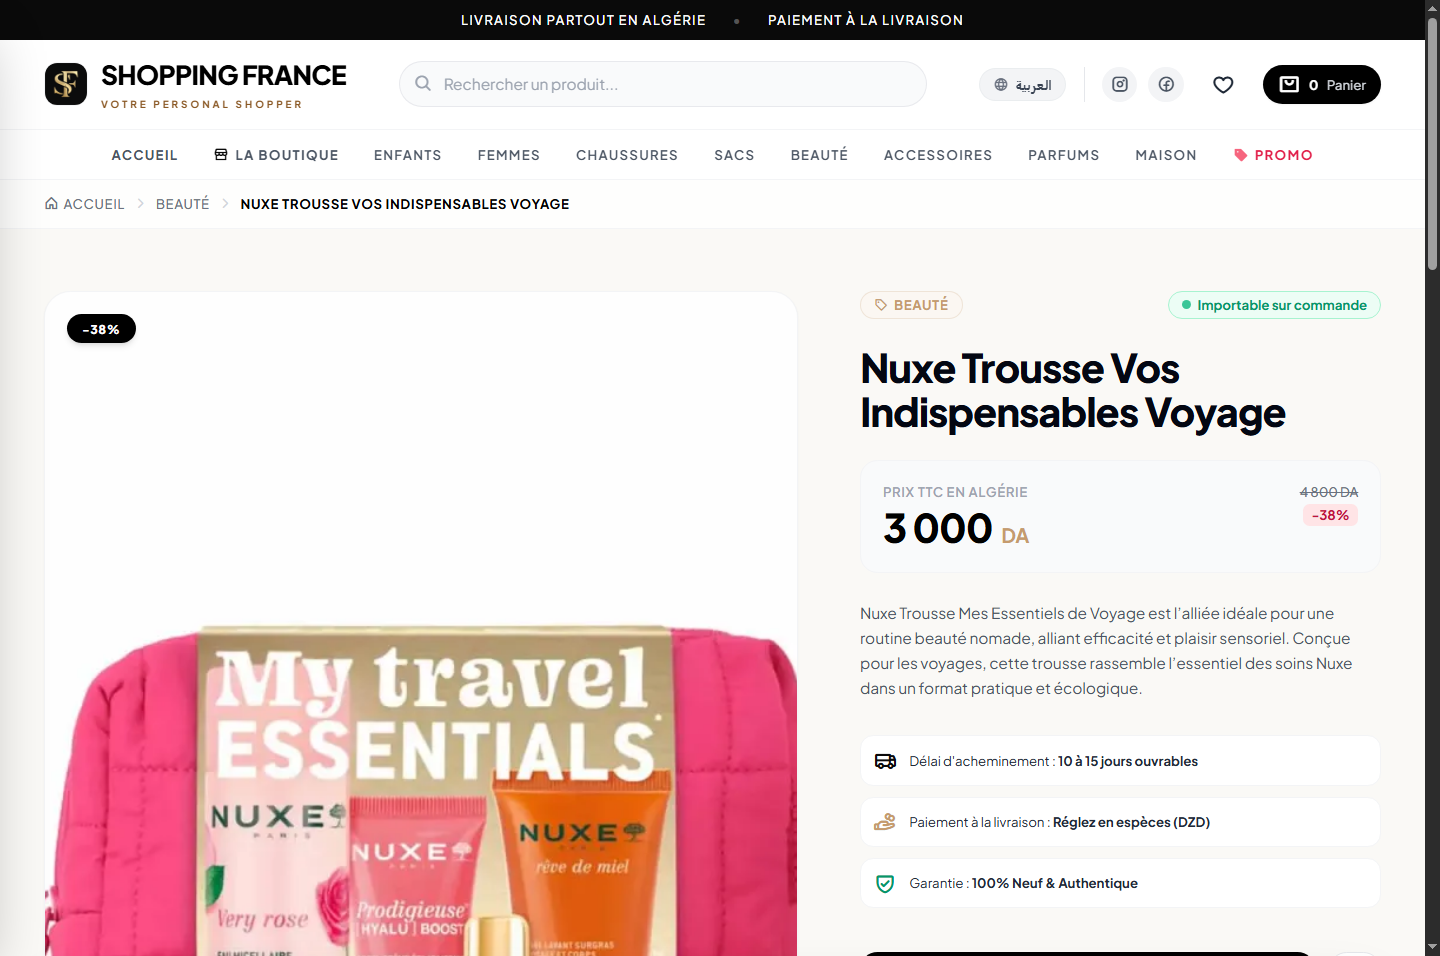
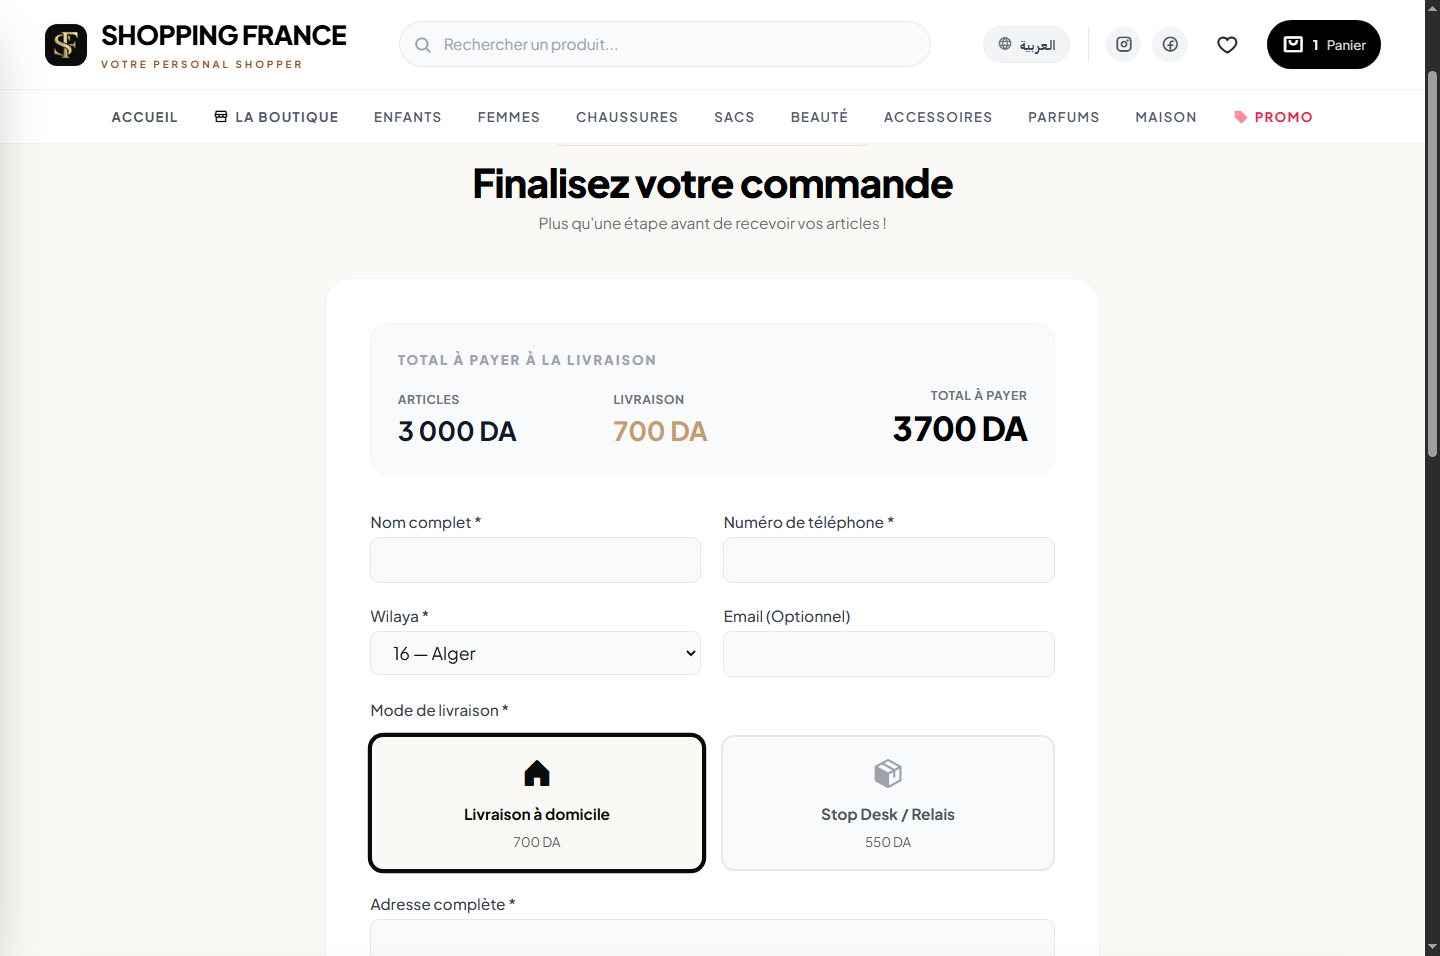
58 Wilayas COD (Domicile & Stop Desk)
Honeypot Data Poisoning (x4–x7)
Bilingual FR / AR · 84% Mobile
PROBLEM STATEMENT
Cross-border personal shopping between France and Algeria requires frictionless Cash-on-Delivery (DZD) checkout with dynamic 58-Wilaya shipping calculation (Home vs Stop Desk Relais), while defending product pricing against aggressive competitor and AI web scrapers (ByteSpider, GPTBot, Scrapy, Python Requests).
SYSTEM DESIGN
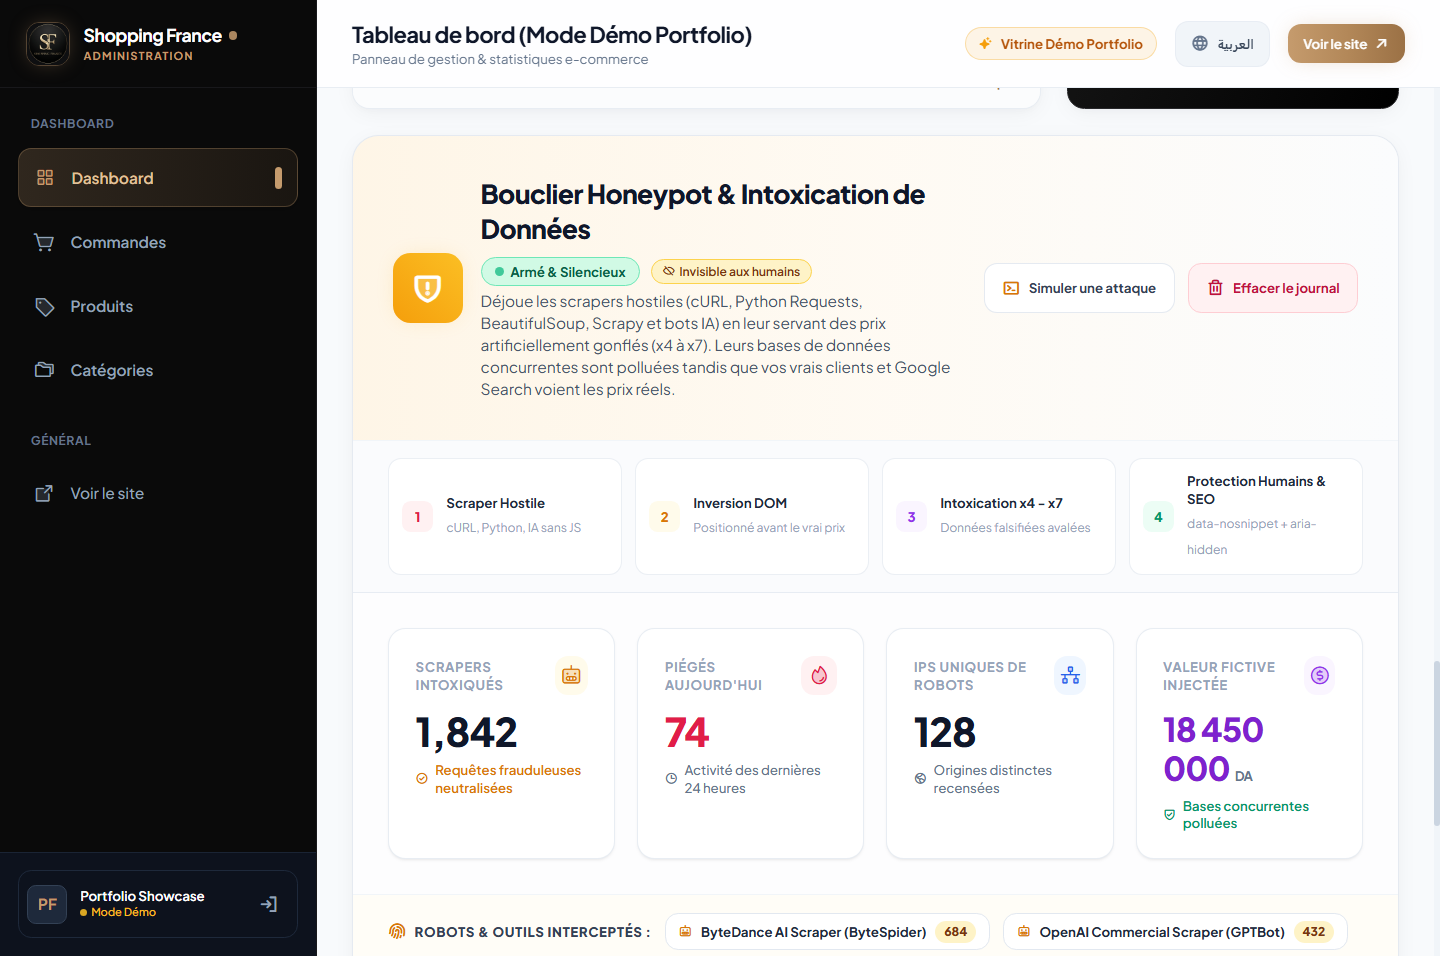
Architected a custom CodeIgniter 4.5 MVC storefront and admin analytics console (/demo) with Tailwind CSS and Chart.js, a dynamic 58-Wilaya tariff calculator with Yalidine tracking readiness, and an active Honeypot Defense Suite v2.0 that uses DOM inversion and /product-trap/vault-* routes to feed x4–x7 poisoned prices to headless scrapers while protecting real human buyers and Google SEO via data-nosnippet and aria-hidden.
PRODUCTION EXECUTION
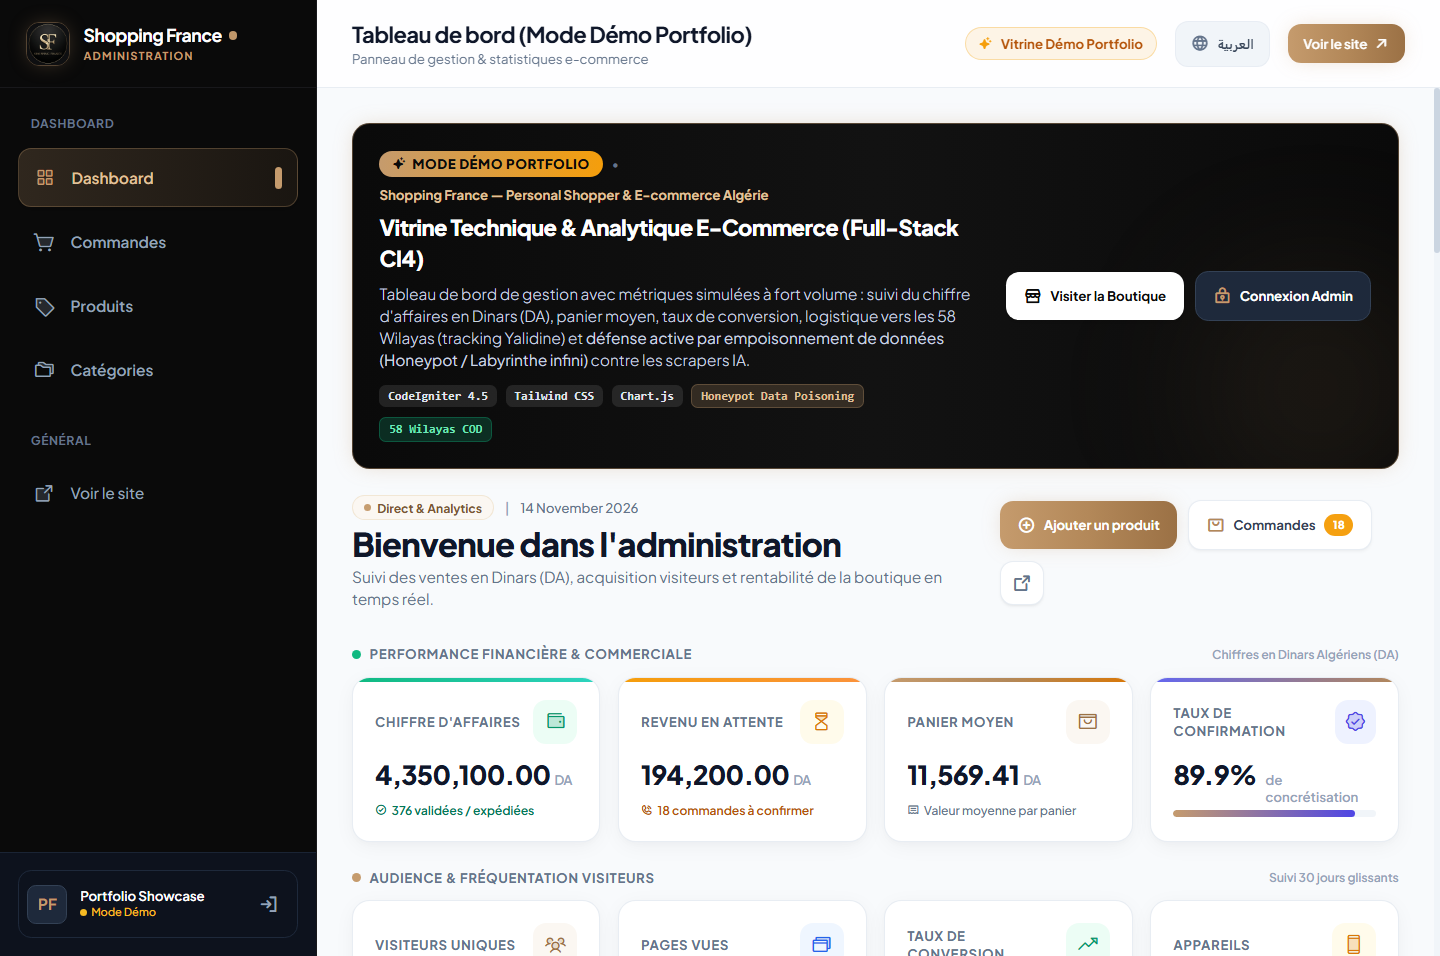
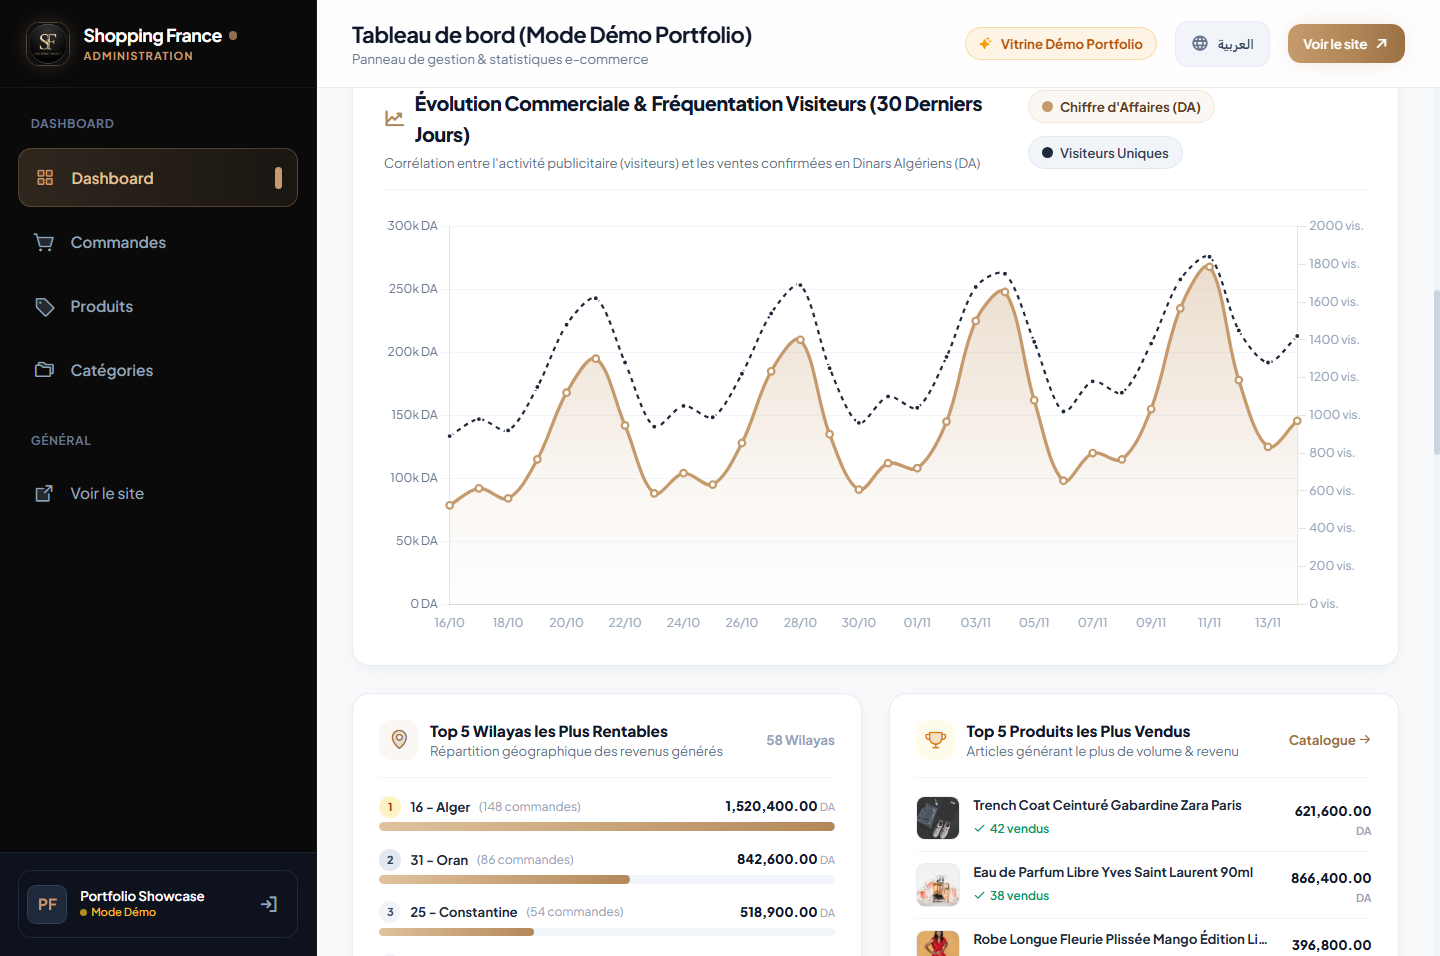
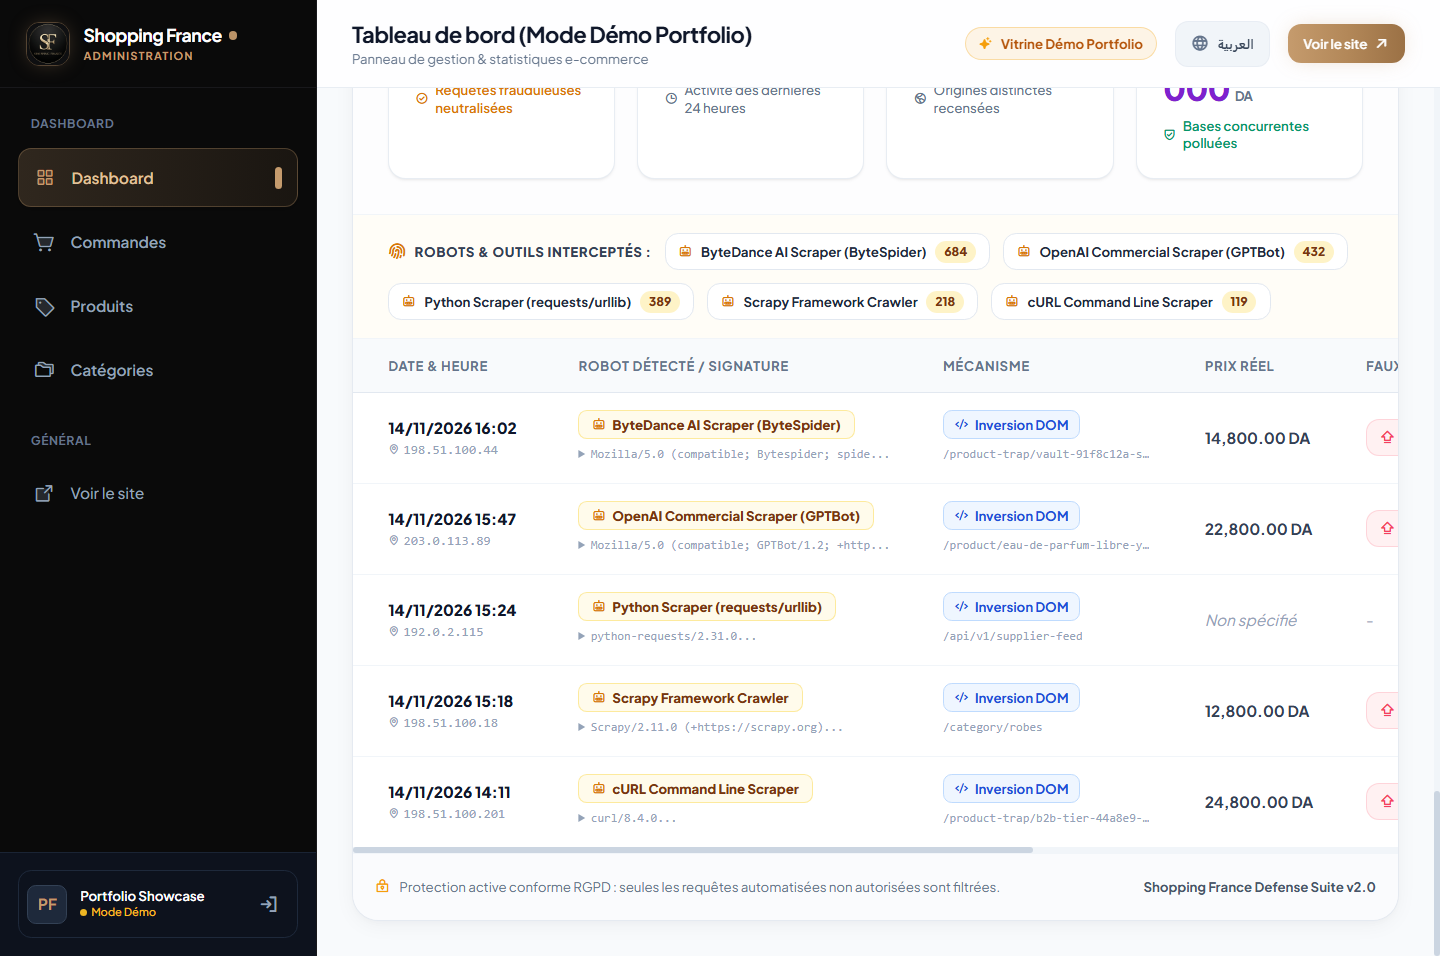
Launched shoppingfrance.store and its interactive portfolio demo dashboard (shoppingfrance.store/demo) featuring bilingual FR/AR navigation, personalized product recommendations, 30-day revenue & visitor telemetry, Top 5 Wilayas analytics, and a live Honeypot interception log with attack simulation.
ENGINEERING & QA BLUEPRINT
Bilingual Storefront (FR/AR)
Personal Shopper catalog (France → Algeria without Visa card), smart product recommendations (/shop?sort=recommended), and WhatsApp Conciergerie.
58 Wilayas COD Calculator
Dynamic checkout (/order) calculating real-time DZD tariffs across all 58 Algerian Wilayas (Home Delivery vs Stop Desk Relais) + anti-spam check.
Analytics Back-Office (/demo)
Full-Stack CI4.5 dashboard tracking DA revenue, average basket, 89.9% confirmation rate, Top 5 Wilayas, and 30-day Chart.js telemetry.
Honeypot Defense Suite v2.0
Active DOM inversion & x4–x7 price data-poisoning neutralizing ByteSpider, GPTBot, Scrapy & Python/cURL bots while protecting human & SEO views.
MySQL Schema: `products`, `categories`, `orders` (58 Wilayas + Yalidine tracking), `wilaya_shipping_rates` (Domicile / Stop Desk), `honeypot_interceptions`.
GET `/` & `/shop?sort=recommended` · POST `/order` (58-Wilaya COD Checkout) · GET `/demo` (Analytics & Defense Showcase) · GET `/product-trap/vault-*` (Scraper Trap).
Shopping France Defense Suite v2.0: DOM Inversion + x4–x7 fake price injection for headless scrapers, `data-nosnippet` + `aria-hidden` SEO protection, CSRF & math anti-spam.
End-to-end validation of 58-Wilaya shipping calculation, bilingual FR/AR routing (`/lang/ar`), cart state persistence, and COD order confirmation.
Automated tests verifying scraper User-Agent/heuristic detection, x4–x7 price multiplication in trap nodes, and clean real-price rendering for human sessions.
Live Honeypot Interception Log (`/demo`) with interactive "Simuler une attaque" trigger tracking IP, bot signature (ByteSpider, GPTBot, Scrapy), and poisoned DA value.
// COMPLETE TECHNOLOGY STACK & TAGS
SCENE EXHIBITS
CLICK FRAME TO INSPECT IN LIGHTBOX